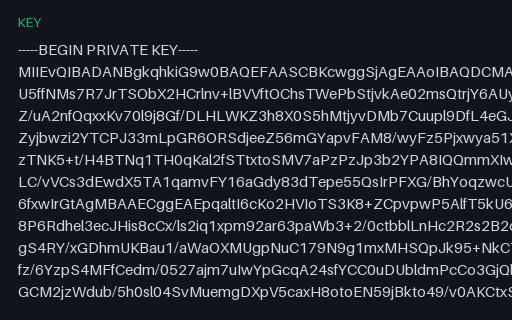
SAMPLE RSA Private Key: PKCS#8, Unencrypted
The SAMPLE leaf's RSA-2048 key in unencrypted PKCS#8 (BEGIN PRIVATE KEY): the modern default and the pair to the PKCS#1 twin beside it. It is deliberately published; treat it as public.
-----BEGIN PRIVATE KEY-----
MIIEvAIBADANBgkqhkiG9w0BAQEFAASCBKYwggSiAgEAAoIBAQC8VD4Uq+k6GCZy
m1SEJmT1CL8tz2CKcEF0dVV9fsYEPUut7eHbMErRm6rMqGteNqD6ExzJFWiXKg+d
+kIaaf4mvZC08ATRSO4bTvBZ/Ujp2GDt08eOR5YATMOpPa1vbjiOdgpU9XNOPtfo
vcFS95l8WIqrMZmnal5BInnoKh7XddJF20NS2gbVVi7nQ+z1AlHqgq/1vS6O4pzt
2Ev95rq9atyBUuCAqPTZq5B6Eupnwc5qybE+mv8tbSRwTAJKFsc9zaqSBntio2hz
FtIH0B07UWfcZFUBxjWG4jecs9DjEvtvOaKKfIRpzSc9F9zLMiu1kj/csdo2tbuV
JsxZf723AgMBAAECggEADz/YXF7PM8pg0pw2lmdwJVHf/nBG+5lmCMK3eWyafB1l
KLWVDuU01GQrywaYKw4hWskmu4w65oKcC8ldMOZZk1QmM4B742EUZqxYVJu9xlxO
/PL5EFGbmR/zd/DBP79HtRa5yhyrNDAX1jCx8Ws7HREjqVkK0r46LkFXEwWAxHwS
S1qEHHZVg9ydIhLUQEGcVFnE3wEd8an5sWhZnoR2BOTLK5l8uCJxq7XLsbDCBMZZ
q0HUcRMH7c1U/REoKsTv6g0wUrsoQqyQNWypUY9zO5au2XlirikWa3koKJ1O/6yL
WKI3X1wlslN2VpPIJecNTXaJ9LQa/oBF2aQCGbmLgQKBgQDdJPWVfPF/oUKmUHMl
7/TDbTMhSV4iX0+ZVIowodqVyFhNu3hAZNZMwu/wfmebsWVuMEtajn5GCz/8qMwx
wvJwpoWUJqvAUppFGyg+Ytfw4bFoffuINdb4yOLld/F6p4b7xMpwiUa6OoSgUv4k
a2C5Us55L6T0fCwpvfFKgomhnQKBgQDaAzSxGde1iaZlZ3oGKdHGCHc/xxj0o3xW
7NMbSRnRqOid7w1skrrFQE92+H7gEc7xhI1GmJiO5fmQQCCflSzT8C9m9DEI3iWO
yxcIBg7XK5tgnY/V88LDVxprA9Hr3JDevZdU622iYQMoAYo3Q44j8/I+iy6d0evm
hjPpYNHWYwKBgFBQEOSGaMpaTXNLOlZny/OBYBVRqN9A0A62di1tSo4lIXSxhd2V
AYMFNNCZh5Uymsymu2ca4t8bTNS8lNPpodSplU+Vr8B7/0zjrPzjNttji+OQBV6V
dwoJIuYFZmyOFOawtHikUkxl3i6/lU6ytID5gsTeOcEUq5FJSy0tNUC9AoGAaPI6
HzbNe/ozO4VAXE8tSCMzJGR3QuygIkgGp4/c+exRbhVxZN6NQf7fQeoFSV/JOsIQ
L/etGLzkEeiMy8VHuw5YAztxj09AzSg+ggJIipPXS/8NCnU5QEdh1DoWh2+53T9u
5dYfBJemqU90dX3zoqL/7dOaMSaoZGQeAS42VPkCgYBswG/QQNhHRlzvll1U3QVp
0QZvQLzG78YJKKA4Abv5zb1gpR2ExDeYLV/x5YukCnOdtCwlVXeFHqY8iMMfL8ZM
mMNBtuhycHetmFk39ArPjlavyYKw24EfrLxyo9MRmOD+HRr6/Z/ASaBuO13Fu5Du
OnoxpHjddNUeQ7RsB3Lt/A==
-----END PRIVATE KEY-----
Specifications
- Algorithm
- RSA
- Bits
- 2048
- Container
- PKCS#8
- Armour
- BEGIN PRIVATE KEY
- Encrypted
- false
- Matches
- the SAMPLE leaf certificate
- Warning
- published sample key: never use for a real identity
- Sample Only
- true
- Seed
- 70117
Testing contract
Expected to pass- Scenario
- Load the key and confirm it is the private half of the SAMPLE leaf certificate.
- Expected result
- The key parses as RSA-2048 and its public modulus equals the leaf certificate's SubjectPublicKeyInfo modulus.
What is a .key file?
A .key file holds a private key, usually PEM-encoded in PKCS#8 (BEGIN PRIVATE KEY) or a key-type-specific format. It is the secret half of a TLS or SSH identity and must normally be protected. The examples here are published, sample-only keys that must never be used in production.
How to use this file
Use an example .key to test PEM key parsers, PKCS#8 decoders, and key-format converters (for example PEM to DER or OpenSSH). These are deliberately published sample keys, for parser testing only, never for real use.
How to use this file for testing
“SAMPLE RSA Private Key: PKCS#8, Unencrypted” is a deterministic Testaroo fixture for Certificate & key testing. Self-signed X.509 certificates (PEM, CRT, DER), a CSR, RSA and Ed25519 keys, an SSH public key, a PKCS#12 bundle, and an htpasswd file, all published sample-only material, for testing certificate parsers, TLS tooling, keystore importers, and PEM/DER decoders.
Documented properties for this file: seed 70117 · RSA. Compare results against paired or grouped companions on this page when present (clean↔damaged, searchable↔scanned, or format twins) so scores stay reproducible across runs.
Download the file once, keep the path stable in CI or local scripts, and treat the spec table as the contract: dimensions, seeds, field lists, and roles are intentional. Corrupt or invalid samples are labelled as such, expect parsers to fail loudly rather than silently accept them.
This is published, SAMPLE-only security material, never a real secret. Point certificate, key, or token parsers at it, test PEM/DER decoding and PKCS handling, and confirm your tooling reads the documented fields; any sample password is printed on this page.
This is a published, sample-only certificate/key. Parse it, verify the chain or signature, and test PEM↔DER conversion, never deploy it anywhere real.
Generated by generation/security_p7.py. Free for any use, no attribution required, license.
Related files
- jsonCRL Metadata JSON: SAMPLESAMPLE CRL metadata JSON (no binary CRL) for revocation-list UI and loader tests.
- keyEd25519 Private Key (PEM): SAMPLEDeterministic SAMPLE Ed25519 private key for SSH/TLS tooling tests.
- keyEncrypted PKCS#8 RSA Key: SAMPLEPassword-encrypted SAMPLE PKCS#8 private key (password printed in specs) for decrypt-import tests.
- csrPKCS#10 CSR: Security SAMPLEPKCS#10 certificate signing request SAMPLE for CSR parsers and CA tooling smoke tests.
- p12PKCS#12 Bundle (.p12): SAMPLESAMPLE PKCS#12 keystore (password `novus-sample-wg`) for keystore importer tests. Not byte-stable.
- keyRSA-2048 Private Key (PEM): SAMPLEPublished SAMPLE RSA-2048 private key (PKCS#8 PEM). Never use for a real identity.