Skip to content
Testaroo

Supply chain

Software supply-chain tooling reads a small family of documents very carefully, and getting a realistic one to test against usually means scanning a real product. This category ships them outright: CycloneDX and SPDX SBOMs in JSON, XML, and tag-value form, describing the same fictional component tree so format converters can be diffed. Lockfiles cover the major ecosystems with pinned versions and integrity hashes. Provenance and attestation fixtures follow the in-toto and SLSA shapes, VEX and OSV documents carry advisory data for invented packages, and dependency-audit reports show the output a scanner would produce. Every package name, version, hash, and advisory ID is fabricated, realistic in shape, and traceable to nothing real.

Filter supply chain on Browse · 116 files · 5 subcategories

Results start with a representative from each related test family. Use a card’s variant menu or the filters below to reach a specific format, profile, or failure case; every sample retains its own detail page and download.

Frequently asked questions

Which SBOM formats do you ship?

CycloneDX in JSON and XML, and SPDX in both JSON and tag-value form, all describing the same fictional component tree, so format converters can be diffed against a known target.

Are the package names and advisory IDs real?

Never. Components, versions, hashes, licences, and advisory identifiers are fabricated to be realistic in shape while referring to nothing that exists.

Do you include provenance and vulnerability documents?

Yes, in-toto and SLSA-shaped attestations, VEX and OSV documents, dependency-audit reports, and lockfiles with pinned versions and integrity hashes.

Start with one example from each use-case group, then continue through its other test families. Choose a use case, search, or filter to find a specific profile; a card’s variant menu contains its related samples.

Filter these files
More filters and sorting
More file filters

Results

15 test families · 116 available files · Page 1 of 1

Preview of cargo tree Output

Graphs

cargo tree Output

Cargo's tree output, which writes versions with a leading `v` and marks already-shown subtrees with `(*)`: close enough to npm's tree to fool a parser, different enough to break one. Every package, version, hash and lice

File
TXT · Graphs
Preview of bun.lock (Text Lockfile)

Lockfiles

bun.lock (Text Lockfile)

Bun's text lockfile, where each package is a positional array of descriptor, dependency map and integrity string rather than an object: a shape that breaks parsers assuming every lock entry is keyed. Every package, versi

File
LOCK · Lockfiles
Preview of Attestation Verification Policy (YAML)

Provenance

Attestation Verification Policy (YAML)

The policy an admission controller evaluates before an artifact is allowed through: required predicate types, an allowed-builder list, a minimum SLSA level, a transparency-log requirement and one dated exception. Every p

File
YAML · Provenance
Preview of CycloneDX 1.4 Application SBOM (XML)

Sbom

CycloneDX 1.4 Application SBOM (XML)

A CycloneDX 1.4 XML SBOM of the same fictional tree: the version most long-lived tooling emitted first, kept for backwards-compatibility tests against the 1.5 and 1.6 documents in this family. Every package, version, has

File
XML · Sbom
Preview of cargo-audit Report (JSON)

Vulnerability

cargo-audit Report (JSON)

A cargo-audit report that shows three findings while a fourth is on the ignore list, plus an unmaintained-crate warning, so a gate must decide whether warnings count against it. Advisory identifiers use the invented NOVU

File
JSON · Vulnerability
Preview of Dependency Graph (GraphML)

Graphs

Dependency Graph (GraphML)

The dependency graph in GraphML, with typed attribute keys for node version, licence and depth and for edge range: the interchange format graph databases and analysis tools import. Every package, version, hash and licenc

File
GRAPHML · Graphs
Preview of Cargo.lock (version 3, Legacy)

Lockfiles

Cargo.lock (version 3, Legacy)

The same fictional Rust tree pinned by a version 3 Cargo.lock, for testing that a reader keys on the declared version rather than assuming the newest format. Every package, version, hash and licence is fictional: the tre

File
LOCK · Lockfiles
Preview of Detached Signature, ASCII Armor: SAMPLE Shape

Provenance

Detached Signature, ASCII Armor: SAMPLE Shape

An ASCII-armored detached signature block of the shape that accompanies a SHA256SUMS file. It is a SAMPLE placeholder, not a valid OpenPGP signature: armor detectors will find it, verifiers must reject it. Signatures, ke

File
TXT · Provenance
Preview of CycloneDX SBOM With Schema Violations: Intentionally Invalid

Sbom

CycloneDX SBOM With Schema Violations: Intentionally Invalid

An intentionally invalid CycloneDX SBOM: the JSON parses, but bomFormat is missing, one component has no name, and a dependency references a bom-ref that no component declares. Every package, version, hash and licence is

File
JSON · Sbom
Preview of CSAF 2.0 VEX Document

Vulnerability

CSAF 2.0 VEX Document

A CSAF 2.0 VEX advisory with the nested product tree that CSAF requires (vendor, product name, product version), and product_status buckets rather than a per-statement status field. Advisory identifiers use the invented

File
JSON · Vulnerability
Preview of Dependency Graph With a Cycle (Graphviz DOT)

Graphs

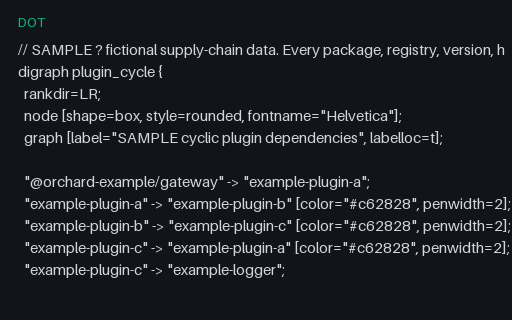
Dependency Graph With a Cycle (Graphviz DOT)

The cyclic plugin graph as DOT, with the three cycle edges highlighted. Graphviz renders it happily, which is exactly why a topological sort must be the thing that rejects it. Every package, version, hash and licence is

File
DOT · Graphs
Preview of npm Lockfile With a Peer Conflict and Nested Duplicate

Lockfiles

npm Lockfile With a Peer Conflict and Nested Duplicate

An npm lockfile where the fictional example-cache pins a peer of example-logger@2.9.0 while the rest of the tree resolves 3.4.1, forcing a nested node_modules duplicate: the shape a deduplication report must detect. Ever

File
JSON · Lockfiles
Preview of Rekor Transparency-Log Entry

Provenance

Rekor Transparency-Log Entry

A transparency-log entry keyed by its own UUID at the top level (a shape that breaks parsers expecting a fixed root key) with a base64 body that decodes to a dsse record. Signatures, key ids and certificates here are SAM

File
JSON · Provenance
Preview of OSV Record With Schema Violations: Intentionally Invalid

Vulnerability

OSV Record With Schema Violations: Intentionally Invalid

An intentionally invalid OSV record: the JSON parses, but the required id is missing, modified is not an RFC 3339 timestamp, the SEMVER range has a fixed event with no introduced event, and severity.score is a number whe

File
JSON · Vulnerability
Preview of npm package-lock.json (lockfileVersion 1, Legacy)

Lockfiles

npm package-lock.json (lockfileVersion 1, Legacy)

The original npm v1 lockfile layout (a nested dependencies object with requires maps and no packages section) still found in long-lived repositories and needed by any migration path. Every package, version, hash and lice

File
JSON · Lockfiles

The use-case group filter replaces the long list of category sections.